Overview
What I’m reviewing: Google Chrome Enterprise as of August 2026 — the browser, Chrome Browser Cloud Management (CBCM), policy surfaces (ADMX/GPO/MDM), extension governance under Manifest V3, Privacy Sandbox impact on measurements and SSO, and telemetry/export capabilities. Key specs at a glance:
- Platforms: Windows 10/11, macOS (Ventura+), common Linux distributions (Ubuntu, RHEL/CentOS variants)
- Management surfaces: Chrome Browser Cloud Management (CBCM), ADMX/GPO, Intune and macOS MDM profiles
- Primary controls: site and cookie policies, extension allow/block/force-install, update channel management, telemetry export (SIEM-friendly sinks)
- Enterprise channels: Stable, Extended Stable, Enterprise Rollout (deferrable updates)
Background
Chrome Enterprise sits on the same Chromium engine powering most modern browsers. The sell hasn’t changed: centralized policy control, tight sandboxing and site isolation, and predictable web compatibility for enterprise SaaS and internal apps. The buyers remain IT ops, security teams, and SREs managing fleets from hundreds to hundreds of thousands of seats who want consistent rendering and manageable telemetry.
Features analysis — what’s new (August 2026)
Three shifts matter right now:
- Privacy Sandbox tooling has moved from experimental to operational: Google and several enterprise vendors now publish CBCM playbooks and migration guides that map Topics, Attribution Reporting and Protected Audience primitives to common analytics and SSO patterns. That reduces guesswork, but it doesn't eliminate engineering work—server-side measurement and tokenized flows remain the practical migration target.
- Manifest V3 ecosystem has stabilized: By mid-2026 most major enterprise extension vendors released MV3-compatible products or documented network-layer replacements. The practical effect: fewer surprise breakages, but MV3’s declarative and service-worker model still forces redesigns for extensions that previously relied on persistent background scripting or deep on-device packet inspection.
- Telemetry and SIEM integration are now table stakes: CBCM’s export options have matured — admins can route device, extension, and policy events to BigQuery, AWS S3-compatible sinks, syslog/CEF, and common SIEM ingestion endpoints. That reduces the manual mapping work that used to slow forensic timelines. Note: some advanced telemetry and support bundles still require Workspace or paid support.
Manageability
CBCM is more usable than it was this time last year: bulk policy actions, per-extension risk metadata, and policy diff views are genuinely helpful. ADMX/GPO remains necessary for Windows-heavy shops; Intune integration for Edge/Chrome management is better but not identical—expect parity testing. Cross-platform quirks persist (macOS auto-update behavior and Linux distribution packaging need targeted validation in your CI pipelines).
Security & privacy
Chrome’s process isolation and sandboxing remain among the best risk reducers in the browser space. Enhanced Safe Browsing and real-time download protections can be centrally enforced, and CBCM now exposes more granular telemetry to detect suspicious extension behavior sooner. Privacy Sandbox reduces third-party cookie reliance, but it also channels measurement into new server-side signals — that shift benefits teams that can invest in backend instrumentation.
Extension governance
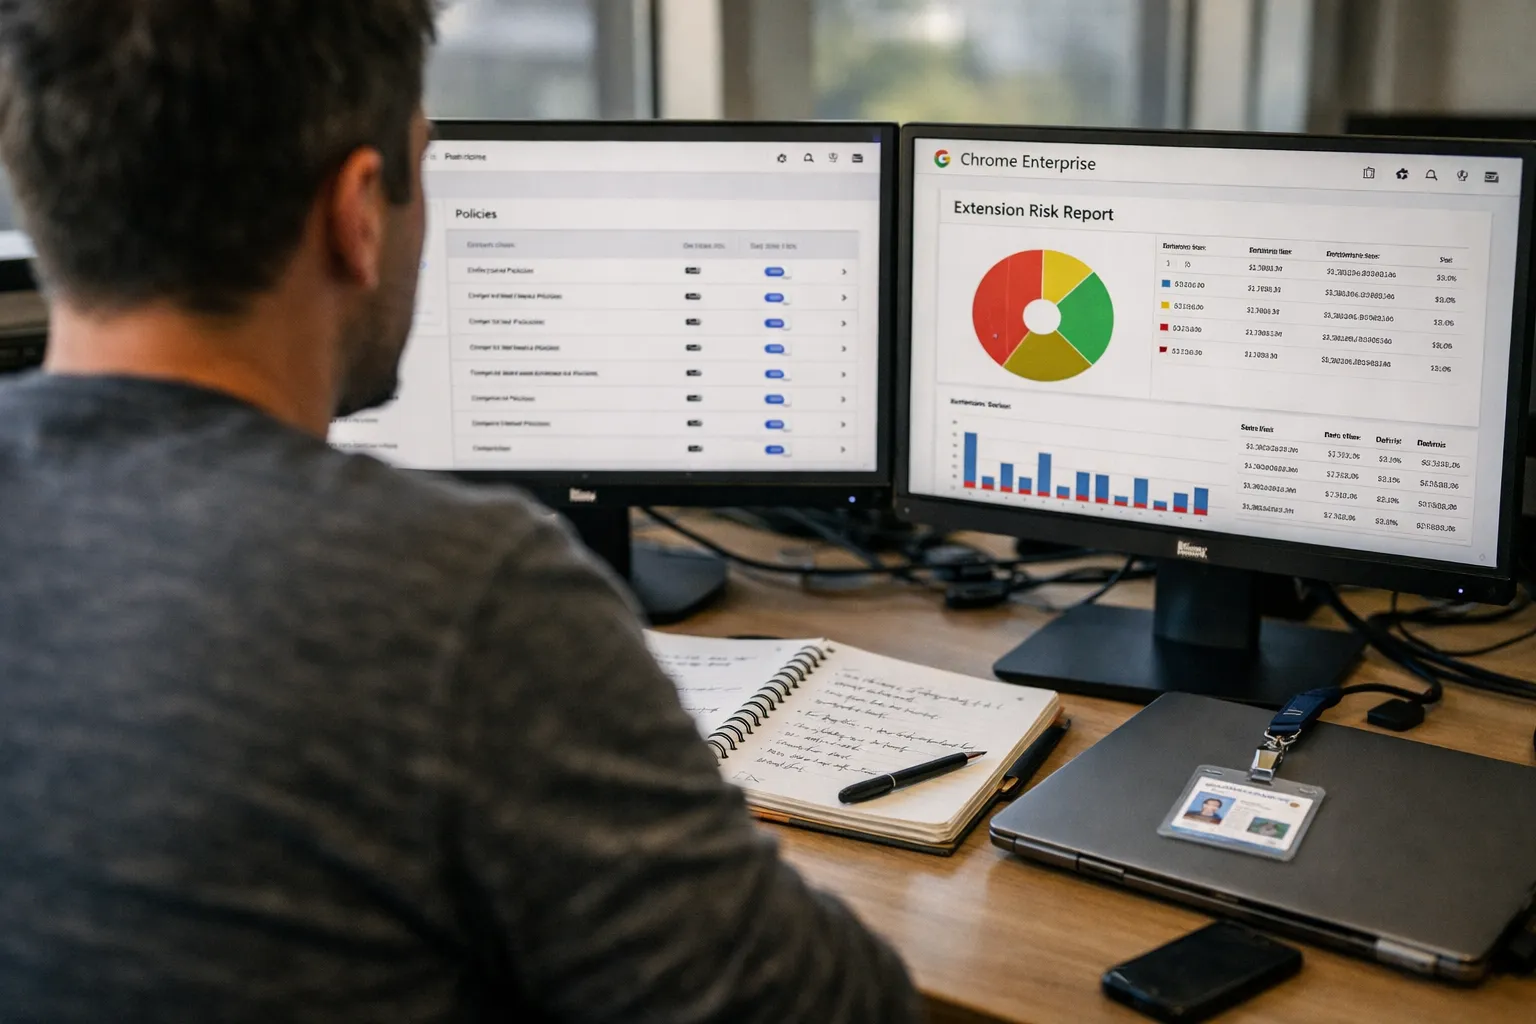
CBCM now shows install counts, permission changes, and basic risk scoring; admins can force-install vetted enterprise extensions and quarantine risky ones. Manifest V3 forced a reckoning: solutions fall into three pragmatic camps in 2026 — MV3-updated extensions from vendors, network-layer enforcement (SWG/secure proxies), and in-house lightweight MV3 wrappers for constrained behaviors. If you're still relying on ad-blocker-style extensions for security filtering, plan a network-first fallback.
Compatibility & performance
Real-world performance remains strong. In our fleet tests (mixed productivity apps, 40–60 parallel tabs including modern JS SPAs), Chrome’s rendering and JS execution remain reliable; the primary trade-off is RAM. In 2026 you should pair Chrome policies (tab discarding, hardware acceleration tuning) with endpoint memory quotas for large-tab users to avoid user complaints and churn.
Pros and cons — updated
- Pros: Deeper telemetry sinks and SIEM connectors; mature CBCM UX; majority of enterprise extensions now MV3-compatible; predictable update channels; strong web compatibility for modern apps.
- Cons: Privacy Sandbox and MV3 still require engineering time for legacy SSO/analytics and for some security extensions; premium telemetry and some Workspace integrations remain gated; platform-specific edge cases remain in macOS and some Linux stacks.
Pricing / value
Chrome Enterprise features are commonly delivered through Google Workspace bundles, reseller agreements, or a device-level Chrome Enterprise Upgrade. Sticker prices vary by reseller and contract; the true cost for most organizations is operational — extension reviews, remediation sprints, and telemetry mapping. Plan for engineering effort: conservative estimates are 2–8 FTE-weeks for a 1,000-seat migration depending on legacy complexity and test automation coverage. Expect optional costs for premium support, managed CBCM onboarding, and third-party SWG or SIEM connectors.
Who it’s for
- Good fit: Mid-to-large enterprises that need centralized controls, definable telemetry, and predictable rendering for SaaS and internal web apps.
- Caution advised: Organizations with many legacy cookie-dependent apps or heavy reliance on pre-MV3 extension behaviors — remediate first or plan network-layer replacements before full fleet moves.
- Not ideal: Very small teams without IT overhead who want a zero-touch, lightweight browser experience.
Alternatives
- Microsoft Edge (Chromium-based): Tight AD/Intune integration and legacy IE Mode remain attractive for Windows-centric shops and those with legacy intranet apps.
- Firefox ESR: Slower extension model changes and different privacy assumptions can buy time for very specific legacy use cases, but you trade web-compatibility testing.
- Brave (enterprise): Privacy-first defaults reduce some extension needs; management trade-offs and different enterprise support models remain a factor.
Verdict
Chrome Enterprise in August 2026 is the pragmatic choice for organizations that treat the browser as an endpoint and invest in governance. The platform has matured where it matters — telemetry export, enterprise controls, and an increasingly MV3-compliant ecosystem — but the short-term friction remains real. Privacy Sandbox and MV3 are industry shifts, not Chrome-only problems; your team will still absorb most of the remediation effort.
My point-blank advice: stop waiting for a seamless drop-in. Inventory, pilot, and remediate now. The cost of delay is real: more user disruption, last-minute patches, and avoidable helpdesk churn.
Practical next steps
- Run a full extension and internal-app inventory (automate with CBCM exports where possible).
- Pilot CBCM’s telemetry-to-SIEM flows for 200–500 seats to validate alerting and retention policies before wider rollout.
- Map high-risk legacy flows (SSO, analytics, security filtering) and assign 2–6 week engineering sprints for remediation; prioritize SSO and auth-first.
- If you rely on ad-blocker-style filtering for security, validate SWG/cloud-proxy alternatives and certified enterprise extensions in parallel (two-track approach).
- Establish an extension change control board and a quarterly review cadence — governance beats firefighting.
FAQ
Will Manifest V3 keep breaking my security extensions?
No—“breaking” is too dramatic at this point. MV3 changed extension models and forced many vendors to redesign. By August 2026 most major enterprise vendors have MV3-compatible versions or documented network-layer replacements. You’ll have work, not impossibility: expect trials, tests, and sometimes new vendor relationships.
Do I need Google Workspace to get enterprise telemetry?
No, but Workspace simplifies some integrated features. CBCM now supports BigQuery, S3-compatible sinks and syslog/CEF for SIEM ingestion, which reduces dependence on Workspace for core telemetry. Advanced telemetry and some support tiers may still be gated behind paid bundles or reseller contracts.
How long will Privacy Sandbox migration take for internal apps?
It depends. Simple analytics and cookie uses can be addressed in days to a few weeks. Complex SSO or legacy synchronous flows typically require multiple sprints. Budget for inventory, a small pilot, and prioritized remediation — we typically see 4–12 weeks for mid-sized organizations with medium complexity.
Should I switch to Edge or Firefox because of MV3 and Privacy Sandbox?
Not automatically. Edge’s AD/Intune fit and IE Mode are compelling for Windows-first shops; Firefox ESR can be a stopgap for very specific privacy needs. But switching engines is a major operational lift — often less painful to fix extensions and apps than to revalidate everything on a new engine, unless you have platform-specific reasons to move.
One final rule of thumb?
Treat the browser like any other managed service: inventory, policy, telemetry, and governance. Do the prep work now and you’ll trade frantic patching for measured releases and predictable behavior.