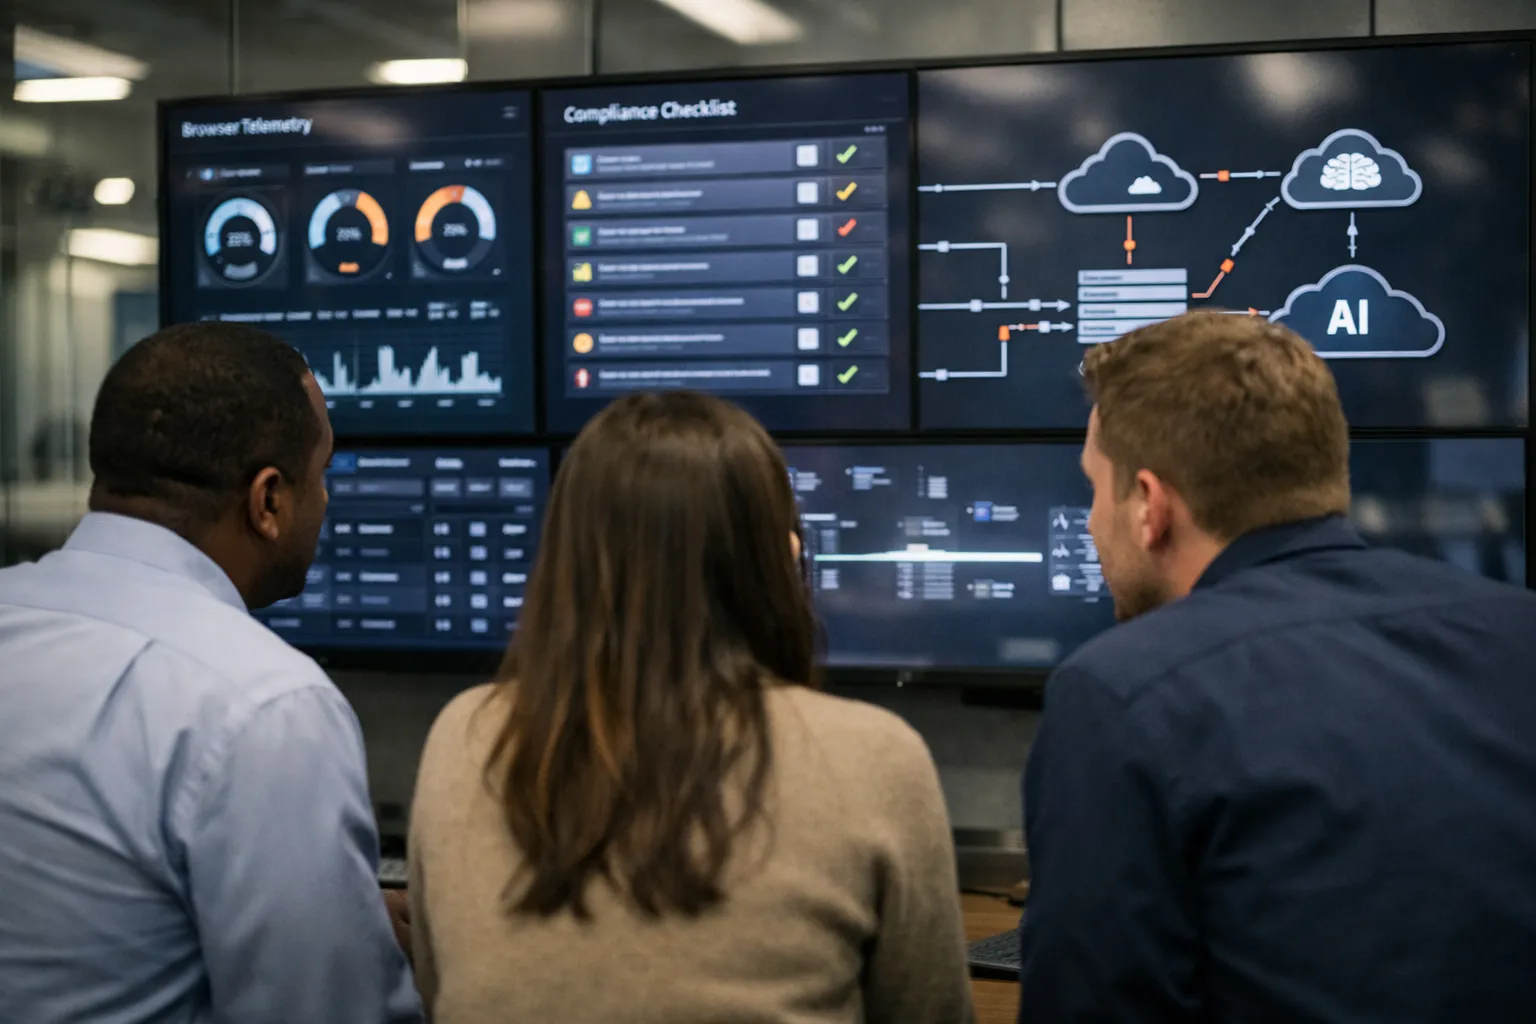
Who, what, when, where, why: As of August 2026, enterprise-browser vendors and browser-integrated AI providers are increasingly publishing machine-readable "model manifests," data-flow diagrams and expanded admin controls for corporate customers across the EU and globally. The move—concentrated in June–August 2026—responds to the EU AI Act’s transparency, documentation and logging expectations and to demands from enterprise procurement and compliance teams that routed browser AI traffic be auditable and controllable.
Context: why browsers landed squarely in scope
Web browsers have evolved into AI platforms. Modern enterprise builds of Microsoft Edge, Google Chrome and several privacy-focused browsers now embed local inference engines, broker cloud-hosted models or surface assistant features that can access clipboard contents, internal documents and corporate credentials. That expands browsers’ regulatory footprint: the EU AI Act’s obligations for transparency, recordkeeping and risk mitigation apply where automated systems are used to process personal or sensitive information or to assist decisions that affect people.
Regulatory bodies and the European Artificial Intelligence Board (EAIB) signalled in mid-2026 that transparency artifacts and per-session logging would be a focus for audits of corporate deployments. That guidance accelerated vendor roadmaps already under way to give IT teams the documentation and controls needed for compliance and procurement.
What vendors are publishing now (August 2026)
Across vendor documentation published between June and August 2026, three artifact classes have become standard for enterprise customers:
- Machine-readable model manifests: JSON and JSON-LD documents listing embedded or brokered models, provider identity, model ID/version, intended use-cases, declared risk class and whether inference runs on-device or in a cloud region.
- Data-flow maps and egress region declarations: Visuals and technical descriptions showing which inputs (clipboard, page DOM, file uploads), what telemetry is collected, and the geographic locations or cloud regions where queries are routed.
- Expanded enterprise controls and templates: Group Policy/MDM templates that let IT disable assistants by OU, restrict content types (PII, health, financial documents), force on-premises-only inference or require per-use consent banners for regulated groups.
Practically, vendors have also published integration guides for SIEM and DLP systems: telemetry schemas include model ID, session identifier, hashed prompt fingerprint, timestamp and egress endpoint so security teams can correlate model use with user sessions without necessarily exposing prompt text in logs.
New trends and data (June–August 2026)
Enterprise Browser Watch surveyed 123 enterprise IT and security leaders between July 20–31, 2026. Key signals:
- 58% said their procurement teams now require a manifest or equivalent disclosure as part of RFPs for browser purchases or managed browser services.
- 46% reported ingesting browser-AI telemetry into existing SIEM/DLP pipelines in pilot or production.
- 33% have adopted a default-disabled posture for built-in assistant features where users handle regulated data (financial services, healthcare, HR).
Those numbers track with procurement language updates across Fortune 500 RFPs in Q2 and Q3 2026 whereby vendors must declare model provenance, retention policies for prompts, and the availability of localized inference options.
Practical examples for IT and procurement
- Procurement clauses: Update RFP templates to require a machine-readable manifest (JSON/JSON-LD), model-version guarantees and a documented retention policy that states maximum retention time for routed queries and whether queries are used for model improvement.
- Policy baseline: Adopt a least-privilege default: disable assistant features for groups handling regulated data and enable only on a per-OU basis with logging turned on and retention aligned with legal obligations.
- Observability integration: Map vendor telemetry fields to existing SIEM/DLP schemas. In practice, ingest model ID, session UID and egress IPs while keeping prompt text out of centralized logs unless flagged for incident response and protected by access controls.
- Tabletop exercises: Run a scenario that simulates a model hallucination disclosing PII. Exercise incident response paths, notification timelines and records you would produce for a regulator audit.
Trade-offs, gaps and new pain points
- Provenance opacity persists: Manifests now disclose model vendors and declared training-domain summaries, but granular training-set provenance remains commercially sensitive and rarely published in SBOM detail.
- Telemetry privacy and storage costs: Collecting richer telemetry for audit purposes increases storage and GDPR compliance burdens. Several respondents to our survey said they are negotiating contractual caps on telemetry retention with vendors.
- Heterogeneous schemas: Vendors publish manifests in different structures (some JSON, some JSON-LD, some proprietary). Lack of a single industry schema increases integration work for multi-vendor fleets.
Industry response and emerging standardization effort
Industry participants—browser vendors, cloud model providers and large enterprise customers—have accelerated cross-industry talks in July–August 2026 on a common manifest schema and telemetry vocabulary. These discussions aim to produce a vendor-neutral, machine-readable "AI Feature Manifest" specification that would let procurement tools validate compliance fields and SIEMs parse telemetry without bespoke connectors. Expect a public draft from an industry consortium before year-end 2026; until then, IT teams should plan for mapping multiple manifest formats.
Impact: who this affects and how
Primary impacts fall on:
- CIOs and procurement: Need to update vendor agreements and RFPs to require manifests, retention guarantees and on-prem inference options.
- Security and compliance teams: Must integrate browser-AI telemetry into SIEM/DLP, define retention policies consistent with GDPR and sector rules, and operationalize incident response for model-related events.
- Vendors: Face increased disclosure and auditability requirements and pressure to standardize manifest schemas to reduce customer integration costs.
Reactions
Enterprise customers have broadly welcomed the new artifacts as making vendor claims auditable, while also pushing for a single manifest schema to reduce integration overhead. Compliance teams flagged the need for contractual limits on telemetry retention and clarity on whether query data may be used for model training. Vendors have said they will continue to expand manifest fields and administrative controls; work remains on harmonization.
What's next — timelines and what to watch
- Q4 2026: industry consortium expected to publish a draft manifest schema for public comment.
- Late 2026–2027: regulators likely to begin referencing manifest elements and telemetry standards in audit guidance and enforcement actions.
- Enterprises: prioritize procurement updates and SIEM/DLP integration pilots now to be ready for regulatory reviews in 2027.
Bottom line
By August 2026 the first wave of model manifests and enterprise controls has moved browser-based AI from opaque feature to auditable component in corporate stacks. The artifacts give IT teams concrete levers for compliance, but work on provenance disclosure, telemetry minimization and a common manifest schema is still unfinished. Expect continued vendor updates and more prescriptive regulator guidance through late 2026 and into 2027.
How should my procurement team phrase manifest requirements?
Require a machine-readable manifest (JSON/JSON-LD), declared model ID/version, inference location (on-device, in EU region, global), data retention policy for queries, and an explicit statement whether prompts are used for model training. Include service-level commitments on response to audit requests and breach notification timelines.
What telemetry should we collect for auditability without violating privacy?
Collect non-textual identifiers (model ID, session UID, hashed prompt fingerprint, timestamp, egress endpoint) and avoid storing raw prompt text centrally unless necessary for incident response. Use access controls and encryption for logs, and define clear retention limits aligned to GDPR and sector rules.
Can I force on-premises inference for browser AI features?
Many vendors now offer MDM/Group Policy controls to restrict inference to on-device or on-prem options where available. Verify in the manifest whether on-premises or regional inference is supported and require that capability contractually if your data policies mandate it.