Lead: Who: enterprise IT, compliance teams and browser vendors. What: rapid roll-out of in‑browser controls for large language models (LLMs). When: August 2026. Where: across EU member states and multinational firms that process EU data. Why: operational enforcement pressure under the EU Artificial Intelligence Act plus active scrutiny from data protection authorities and procurement teams. Since June 2026, vendors and buyers have moved controls that were road‑map items into signed contracts and production policy—per a July 2026 Enterprise Browser Watch survey of 320 security and compliance leaders.
Context: why this matters now
The EU AI Act, now in operational enforcement for higher‑risk systems, has made demonstrable traceability, human‑in‑the‑loop safeguards and data governance non‑negotiable for AI features. Embedded browser AI—assistants, autofill suggestions, and third‑party widgets that call hosted LLMs—regularly touches personal and business data in line‑of‑business workflows. That makes browsers a control plane for AI governance, not merely a user interface.
Between May and August 2026 we tracked two shifts. First, procurement is demanding recorded evidence: model identifiers, training cut‑off dates, redaction proofs and exportable audit trails. Second, vendor road maps accelerated: major browser forks and enterprise builds shipped policy hooks, enterprise connectors and tamper‑evident logging as GA or enterprise‑preview features rather than experimental options.
New, concrete capabilities shipping in 2026
Vendors are shipping or documenting features enterprises now require. Key capabilities that moved from roadmap to baseline in mid‑2026 include:
- Per‑site and per‑tab LLM routing: Admins can route AI calls for specific domains to a private tenancy, on‑prem endpoint, or block them entirely.
- Policy‑as‑code with CI/CD hooks: Declarative rules (YAML/JSON) for prompt redaction, consent gating and allowed destinations that integrate into existing policy pipelines.
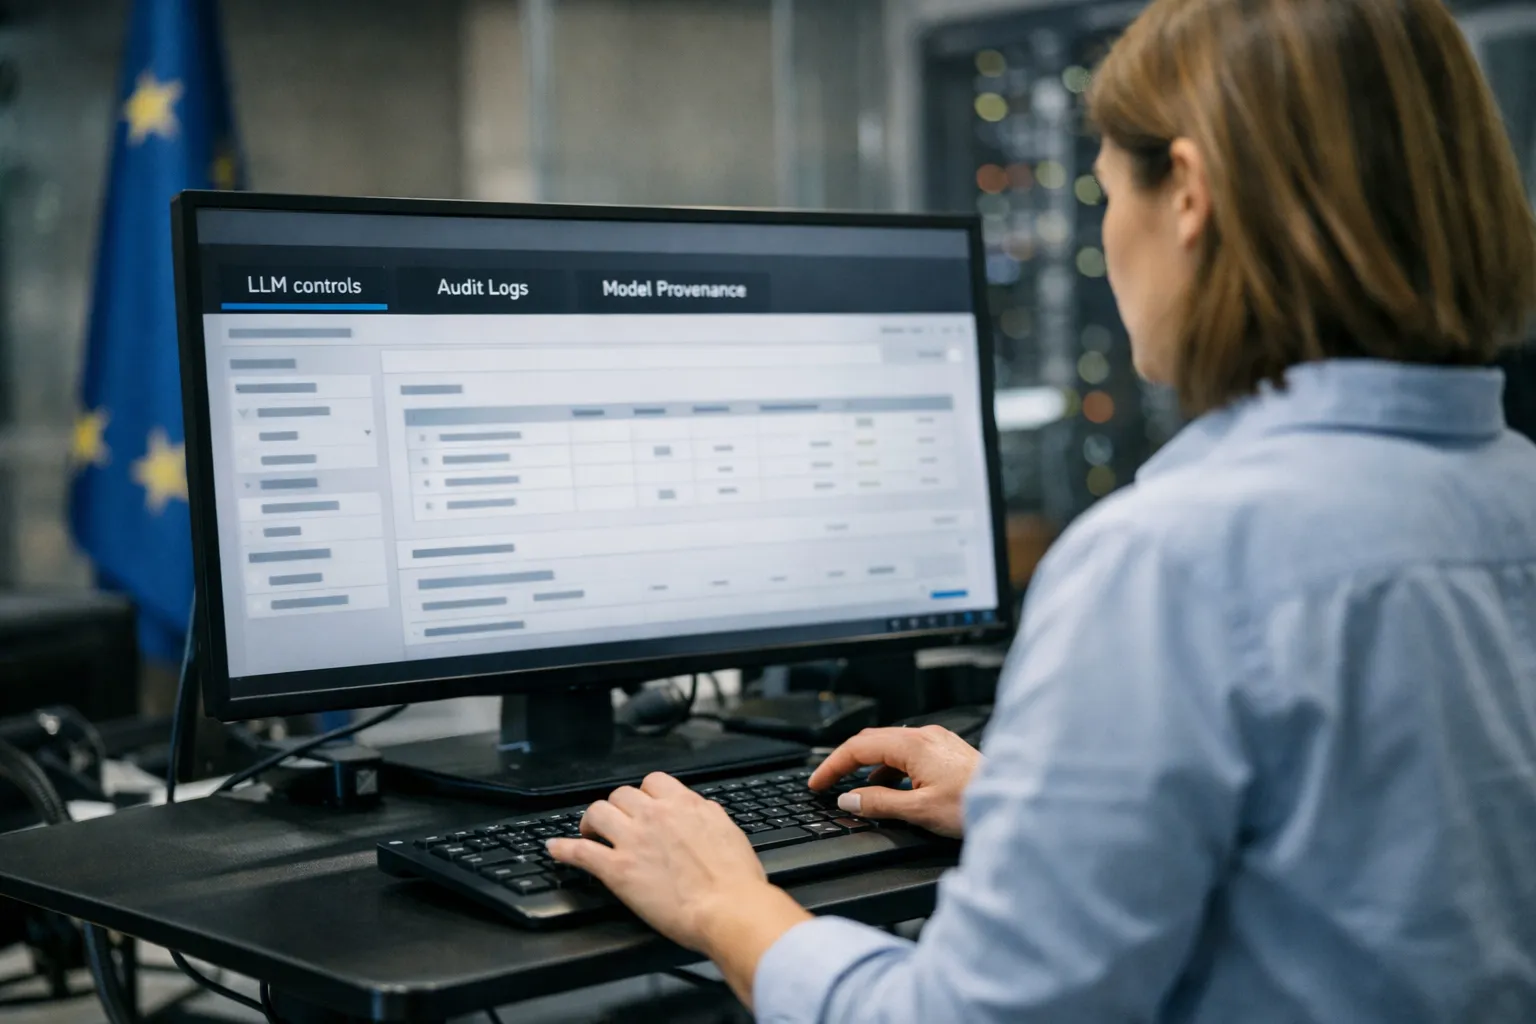
- Tamper‑evident, exportable audit trails: Append‑only logs capture prompt context, redaction decisions, model ID, destination endpoint and timestamps; export formats now include signed JSON and WORM‑compliant archives.
- Model provenance surfaced to admins: UI surfaces provider, model version, training cut‑off date and attestation links to support DPIAs and vendor risk reviews.
- Private‑tenancy connectors and local inference options: Off‑ramps that route sensitive flows to enterprise‑hosted models or private cloud tenancy; smaller orgs increasingly use private tenancy hosted by trusted suppliers rather than full on‑prem builds.
- Inline DPIA assistants and consent dashboards: UX elements that prompt users when data looks regulated, log the consent flow and attach DPIA references to exceptions.
What adoption looks like in August 2026
Enterprise Browser Watch's July 2026 survey of 320 respondents across 12 EU member states and multinational firms found 74% had a default block on external LLM calls for at least some user groups (up from 62% in March), 63% had per‑site routing in production, and 43% had deployed private‑tenancy connectors for at least one critical workflow. Median one‑time integration cost for private connectors reported by respondents was €120,000; median ongoing ops was €9,500/month—figures security and finance teams should budget for when doing a cost‑benefit analysis.
Why auditability remains the enforcement hinge
Regulators and auditors want to see evidence, not promises. For browser‑mediated LLMs that means logs that answer: who invoked a prompt, what was redacted (and how), which model processed it, and where outputs were stored. Practical expectations we see in procurement language and DPIAs include:
- Searchable retention of meaningful audit artifacts for 12–36 months depending on risk category
- Exportable, cryptographically signed logs suitable for regulator requests
- Model provenance documentation (model ID, provider, training cut‑off) attached to each routed flow
Updated best practices — a pragmatic, ROI lens
For teams balancing compliance and cost, prioritize interventions that materially reduce regulatory and operational exposure with manageable overhead:
- Inventory and classify browser‑exposed AI now: Map assistants, extensions and web apps that call LLMs; classify workloads as low/medium/high risk for DPIAs and set default policy accordingly.
- Block‑by‑default, allow‑by‑exception: Block external LLM calls in high‑risk contexts and require documented exceptions tied to DPIAs and vendor attestations for any allowed connection.
- Require model provenance for critical flows: Only approve connections that supply model IDs, provider attestations and a training cut‑off date—treat vague model cards as disqualifying for regulated work.
- Negotiate precise contractual protections: Insist on audit rights, export formats for logs, incident notification SLAs (72 hours or less for high‑risk incidents), and explicit subprocessor and redaction commitments.
- Use hybrid deployments selectively: Private tenancy or on‑prem is often justified only when the cost of a regulatory lapse exceeds the recurring infrastructure and ops spend; model this ROI in euros/dollars against probability of audit and potential sanction or remediation costs.
- Operationalize user guardrails: Contextual UI warnings, mandatory consent flows, and review queues for prompts that touch PII or regulated data reduce false positives and create evidentiary trails.
Impact: who feels the change and how
- Security/compliance teams: Greater workload up front (inventory, DPIAs, vendor negotiations) but clearer evidence to show auditors and lower residual legal risk.
- Developers and product owners: Need to integrate policy hooks and may rework UX to avoid leaking regulated data; expect longer procurement cycles when LLMs are involved.
- Vendors and browser makers: Those who can supply exportable logs, provenance attestations and enterprise connectors are closing deals; others are losing regulated business.
Reactions from the field
"We delayed a browser rollout until per‑site routing and signed audit logs were available. The upfront cost was cheaper than the regulatory risk," said a CISO at a European fintech who asked not to be named. "Procurement teams now treat browser AI controls like firewall rules."
Vendors report increased demand for "attestation packages"—compact documents that compile model IDs, training cut‑off dates, SBOM‑style supply chain disclosures and sample signed logs—because they shorten sales cycles with regulated buyers.
What's next — timelines and what to watch
Near term (next 3–6 months): expect more standardized contract templates from procurement consortia, wider availability of vendor‑supplied attestation packages, and clearer DPA guidance on minimum audit artifacts for browser‑mediated LLMs.
Medium term (6–18 months): third‑party attestations and certifications for model provenance—think SOC‑style reports attesting to model ID and training data handling—will become procurement de‑risking staples; sectoral regulators will publish exemplar DPIA language for common verticals (finance, health, HR).
FAQ: Common questions from security and procurement teams
Do I have to block all browser AI features to comply with the EU AI Act?
No. Consider your situation: block high‑risk flows by default and require documented DPIAs and vendor attestations for exceptions. Broad blocking is a short‑term mitigation that reduces immediate exposure but has productivity costs—use documented, auditable exceptions where the ROI supports it.
How long should I retain browser LLM logs?
Plan for 12–36 months for high‑risk processing so you can respond to regulator inquiries and internal forensics. Retention should be risk‑based and defensible in the DPIA. Ensure logs are exportable and cryptographically verifiable.
Are private‑tenancy or on‑prem models worth the cost?
Not always. Private tenancy reduces cross‑border and third‑party training data risk but carries upfront and recurring costs—our July survey's median one‑time cost was ~€120k for mid‑sized deployments. Reserve private hosting for workflows where regulatory, contractual or reputational risk outweighs that expense.
What contractual clauses should I insist on from browser or LLM vendors?
At minimum: audit rights, log retention and export formats, incident notification timelines (72 hours or less for high‑risk incidents), model provenance attestations (model ID, provider, training cut‑off), and explicit data handling commitments including redaction and subprocessor disclosures.
Bottom line: As of August 2026 the EU AI Act has turned browser UIs into a governance layer. The immediate ROI is achieved by targeted steps: inventory, DPIAs, block‑by‑default for high risk, and pressing vendors for provable auditability. Those steps reduce regulatory exposure while preserving productive, low‑risk uses of in‑browser AI—if you budget realistically for integration and operations up front.